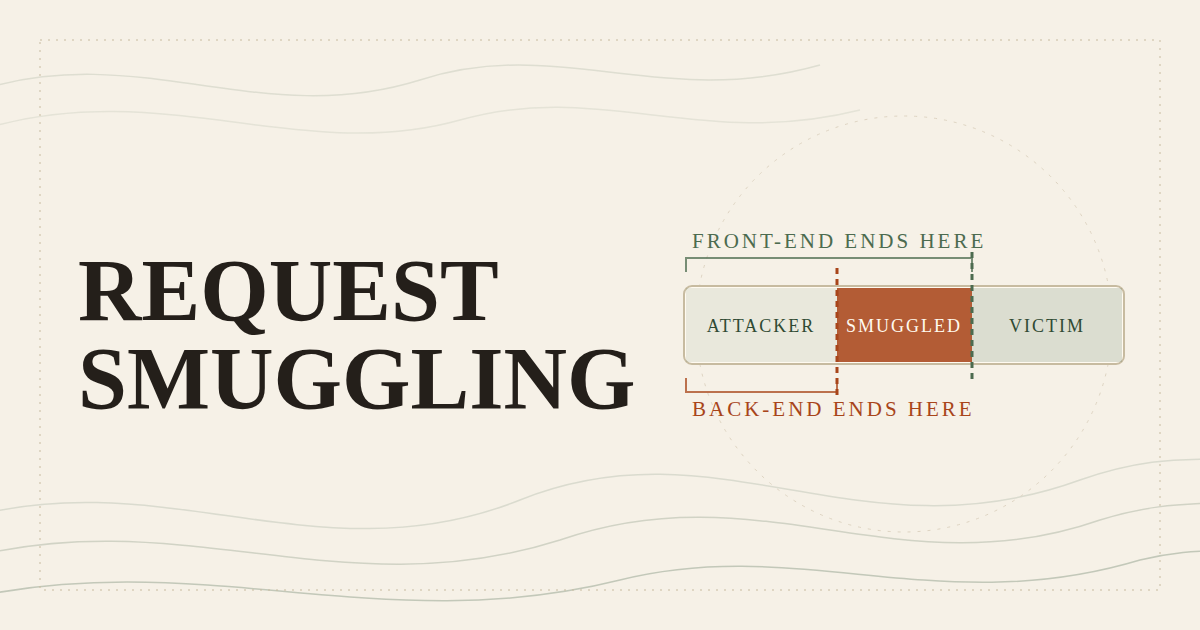
How I Redirected Every App User with Request Smuggling
How chaining a low-severity host header reflection with an HTTP request smuggling bug let me redirect every user on an application and capture admin sessions.
How chaining a low-severity host header reflection with an HTTP request smuggling bug let me redirect every user on an application and capture admin sessions.
An honest review of the GWAPT certification's actual value, how little I studied for it, and why I still don't think teaching you something is the point of a certification.
Burp Suite's built-in browser not launching on Ubuntu 24.04? This post will go over a more secure way to fix it with AppArmor, while avoiding dangerous SUID "fixes" that don't follow the Principle ...
A guide to understanding and differentiating between CL.0 and 0.CL Request Smuggling vulnerabilities, with a practical analysis of testing methodologies.
This article guides you through configuring IntelliJ to start a debugging session with Burp Suite seamlessly at the click of a button. Streamline your workflow and enhance your ability to test Burp...
Refactoring a single-file Python project, like the Burp Upload Scanner, into a modular structure using the MVC pattern enhances collaboration and maintainability. This blog post details the process...
In this HackTheBox walkthrough of the *Boardlight* machine, we explore enumeration techniques, vulnerability exploitation, and privilege escalation to gain root access. By identifying key VHosts, l...
With Firewall Ferret, security testers can now have greater control and precision when testing WAFs, manually adding junk data to requests and expanding Burp Suite’s active scan checks.
Learn how to write JUnit tests for Burp Suite extensions, avoid common pitfalls, and optimize your development workflow.
In this post, I share a Python script that leverages the POC from **CVE-2022-46169** to create a pseudo shell for pentesting, developed as part of a HackTheBox machine challenge. The script automat...